Curriculum Vitae
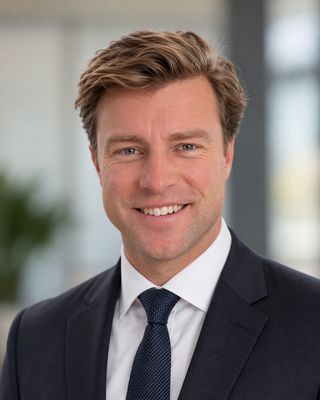
Daniel Polleryd · Governance, risk and compliance · Gothenburg, Sweden
GRC consultant at EY since 2013, working where governance, risk and compliance meet technology. Thirteen years of leading engagements in risk management, internal control, information security, business continuity and internal audit, often enabled by ServiceNow IRM. Experienced project manager, functional architect and audit lead for large Nordic and international organisations, with a current focus on how AI can make GRC work faster and more reliable, and on how AI itself should be governed.
Core competencies
- Risk management: non-financial and operational risk, cyber and information security risk, IT and ERP risk, third-party risk, risk appetite, aggregation and reporting
- Internal control: ICFR and SOX ITGC, control framework design and calibration, issue management, IPO readiness
- Information security and resilience: NIS2, DORA, ISO 27001, GDPR, business continuity management and business impact analysis
- Internal audit: IT governance, change management, architecture governance and operational resilience audits
- GRC technology: ServiceNow IRM: process and solution design, functional architecture, implementation and roll-out
- Management systems: ISO 9001, 14001 and 45001
- AI and data: EU AI Act, LLM-supported regulatory analysis, controls analytics on ERP data (Infor M3), SQL, Python and TypeScript
- Delivery: project and programme management, onshore/offshore teams, workshop facilitation, executive and board reporting
Experience
EY · Consulting
September 2013 – present · Gothenburg
Selected engagements:
Internal Audit Lead · Swedish payment infrastructure company
October 2024 – present
Leads internal audits of IT change management across the client's technical environments, covering governance, mandates, risk assessment, testing evidence, traceability, regulatory compliance and remediation follow-up. Defines and validates scope, plans fieldwork, leads interviews, tests evidence and reports findings. In autumn 2026, leads audits of architecture governance and of core clearing and settlement processes, including business continuity.
Functional Architect · Swiss manufacturing company
July 2025 – September 2026
ServiceNow implementation for information security compliance of the application portfolio and for third-party risk. Owned the high-level design and key architectural decisions, aligned stakeholders on requirements, and worked with ServiceNow on design and licensing questions in a complex stakeholder landscape.
Project Manager · Nordic consumer products company
November 2025 – May 2026
Global governance and internal controls transformation programme covering ICFR, risk management and governance. Maturity assessments in the USA, China, Japan and South Korea; governance framework, policies and procedures; control implementation; and data analytics to identify control weaknesses. Managed delivery and project economics, coordinated Finance, IT, Legal and HR, and reported to senior management and the board.
Information Security SME · Swedish manufacturing company
January – April 2025
Design of an information security risk framework for a global matrix organisation, driven largely by NIS2: roles and responsibilities, aggregation, reporting and remediation of identified risks.
Project Manager · Swedish manufacturing company
January – October 2024
ServiceNow implementation to automate and standardise internal control (ICFR) and data privacy (GDPR). Defined processes and workflows, managed agile delivery and drove business roll-out and adoption.
Project Manager · Swedish manufacturing company
October 2022 – March 2023
Company-wide business continuity management process for IT and a supporting ServiceNow tool, covering business impact analyses for business processes, applications and configuration items, and continuity plans.
Project Manager · Swedish manufacturing company
April – July 2022
Design and ServiceNow implementation of a cyber risk management process for the system portfolio, starting with the most critical applications. Coordinated client, onshore and offshore teams through workshops and user acceptance testing.
Project Manager · Swedish banking and insurance group
2022
Re-design of the framework for managing non-financial and operational risk: target state for roles and responsibilities, risk assessment, aggregation, risk appetite and reporting, developed through workshops, interviews and validation across the organisation.
Earlier engagements at EY
- Team Lead, IPO readiness (multiple companies): led the IT governance workstream, assessing the current state and closing gaps through IT and security policies, controlled IT processes, business impact analyses and continuity management.
- Stream Lead, internal controls calibration (Swedish manufacturer): scoping process, monitoring, root-cause analysis and remediation of non-remediated issues, and management reporting.
- Project Manager, ERP risk assessment (Finnish manufacturer): assessed the risks of a legacy custom ERP and vendor lock-in to support the decision on future ERP strategy.
- Project Manager, management system implementation (nuclear power utility): designed and implemented a management system compliant with ISO 9001, 14001 and 45001 for a new decommissioning subsidiary, through to supplier-audit readiness.
- Project Manager, contract fulfilment assessment (Nordic IT consultancy): independent assessment using document analysis, analytics and interviews.
- Project Manager, information security audits (Swedish municipalities): internal audits of NIS and GDPR implementation, governance and reporting.
Analyst · Accenture, Oslo
2012 – 2013
ERP implementation practice. Part of the team implementing Microsoft Dynamics AX at a large wholesaler, and worked on several bid processes from start to finish.
Selected projects
Fortuna Machinae
This site: a blog on AI for risk management, risk management of AI and AI governance, built and operated with AI tools on a PostgreSQL and TypeScript stack, including an automated regulatory news scanner.
Regulatory obligations register
Structured NIS2 obligations register linked to article-level citations, built for reuse in GRC delivery.
Education
- Chalmers University of Technology: Master's programme in Engineering Mathematics, 2010–2012
- Chalmers University of Technology: BSc in Biotechnology, 2007–2010
- School of Business, Economics and Law, University of Gothenburg: Business Administration
- Tingvalla Upper Secondary School, Karlstad: International Baccalaureate, 2004–2007
Languages
Swedish (native) · English (fluent) · French (basic)